سياسة الخصوصية
1. Introduction
The Disrupt Labs (“Company,” “we,” “our,” or “us”), through its SafetyLens platform, is committed to protecting the privacy, confidentiality, integrity, and security of information entrusted to us by our clients, business partners, and website visitors.
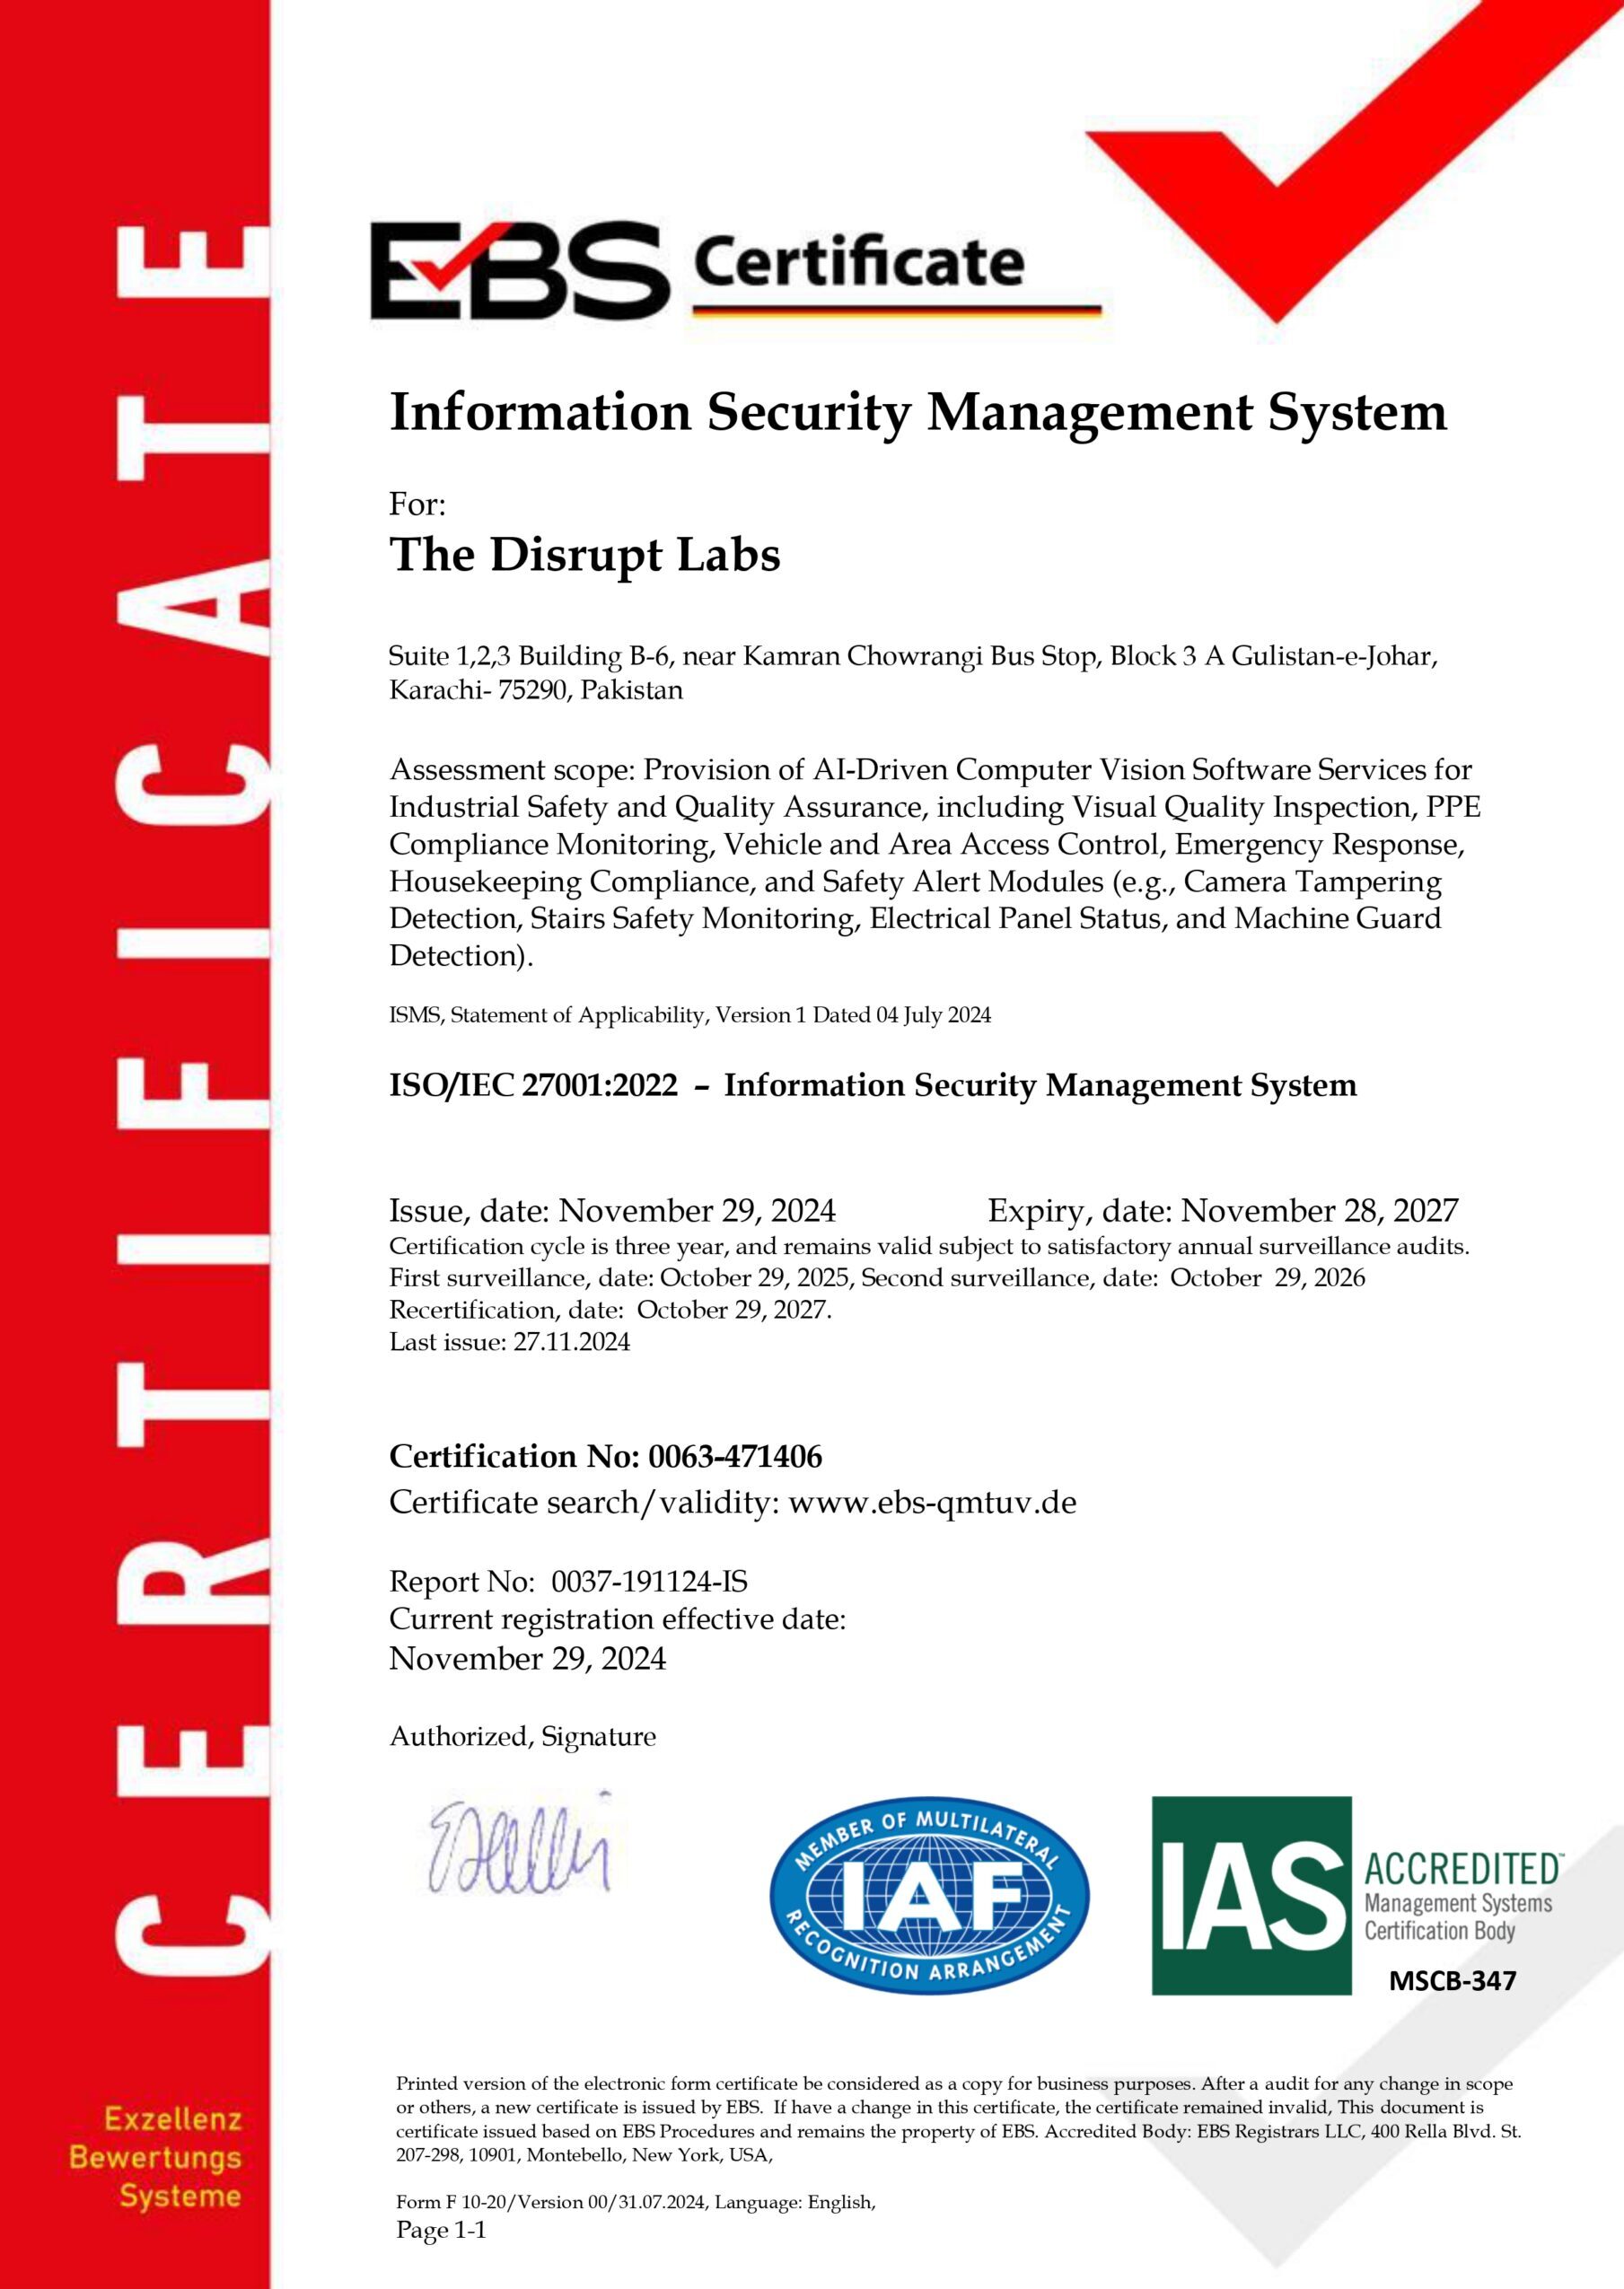
SafetyLens is an artificial intelligence (AI)-powered video analytics and industrial safety monitoring solution designed to enhance workplace safety, improve operational compliance, and identify potential safety risks using computer vision. This Privacy Policy explains how information is collected, used, processed, stored, protected, retained, and disclosed in connection with our website, products, and services. The Disrupt Labs is certified to ISO/IEC 27001:2022 Information Security Management Systems by EBS Registrars LLC. Our certified Information Security Management System (ISMS) supports structured information security risk management within its certified scope.
2. Scope of This Policy
- Visitors to our corporate and SafetyLens websites.
- Client organizations and authorized users of SafetyLens applications, dashboards, and reporting tools.
- Client information processed through AI-enabled safety monitoring.
- Information exchanged during implementation, service delivery, support, and maintenance.
Client-specific contracts, data processing agreements, and applicable legal requirements may establish additional or different obligations for a particular deployment.
3. Information We Collect and Process
Business and contact information: Client organization names, business contact details, authorized users, access roles, support requests, and business communications.
Industrial safety and operational information: Authorized CCTV streams, AI-generated safety observations and alerts, incident snapshots, safety compliance statistics, site and equipment details, and related operational reporting data.
Application and technical information: Authentication and session records, system diagnostic logs, network and device information, and records needed to operate and secure the services.
Website information: Information provided in contact forms and inquiries, and technical information necessary for website operation and security. We seek to limit collection to information necessary for specified, authorized purposes.
4. Client Data Ownership and Control
CCTV footage, operational records, safety observations, and other information supplied by or generated for a client through SafetyLens remain subject to the client’s ownership and control rights under the applicable agreement. The Disrupt Labs does not claim ownership of client operational data.
For client-controlled data, the client generally determines the authorized processing purposes, and The Disrupt Labs acts as a service provider or data processor within the agreed scope. We do not sell client data or disclose it to unauthorized third parties. We do not use client CCTV footage or personal information for unrelated commercial purposes or external AI training without appropriate authorization.
5. CCTV Video Processing and AI Analytics
SafetyLens processes authorized video streams to identify potential industrial safety risks, including personal protective equipment compliance, restricted-area access, unsafe activities, and other configured safety conditions. Processing varies by deployment and agreement:
- For on-premises and supported hybrid deployments, continuous video processing may remain in the client environment.
- SafetyLens may generate alert metadata, reports, event images, and safety analytics.
- Cloud synchronization, where enabled, is limited to agreed information categories and approved destinations.
- The processing location, data flows, and permissions are defined by deployment configuration and contractual arrangements.
AI-generated observations support workplace safety management and may require human review; they should not automatically be treated as conclusive evidence of misconduct or regulatory non-compliance.
6. Purposes of Processing
- Deliver, maintain, and support SafetyLens services.
- Detect and report potential workplace safety risks, and provide dashboards, analytics, and reports.
- Manage access, authenticate users, and protect application and infrastructure security.
- Investigate faults, respond to security incidents, and meet legal and contractual obligations.
- Improve system reliability through authorized operational activities.
7. Data Hosting and Storage
On-premises: Application components, AI processing, databases, and storage may operate on client infrastructure.
Cloud-based: Information may be hosted in approved cloud infrastructure and agreed regions.
Hybrid: AI video processing may remain local while agreed alerts, event images, and reports synchronize to authorized cloud resources.
Hosting locations, data flows, and infrastructure responsibilities depend on the client agreement. We do not intentionally relocate or transfer production client data outside agreed environments without required authorization, except as permitted or required by law.
8. Information Security and Access Controls
Our security management practices, as applicable to the deployment and certified ISMS scope, include:
- Role-based access controls, authentication, and managed access permissions.
- Multi-factor authentication where configured or supported.
- Encrypted transport using HTTPS/TLS and appropriate network restrictions.
- Confidentiality commitments and access limited to authorized personnel.
- Vulnerability management, logging, monitoring, risk assessment, and incident response.
- Backup and recovery measures according to the applicable hosting arrangement.
No technical or organizational measure can guarantee absolute protection against every security risk.
9. Data Retention and Secure Deletion
Data retention is governed by applicable client agreements, approved policies, technical configurations, and legal requirements. Standard configurations may provide for cloud-hosted client data retention of up to one year and on-premises client data retention of up to three months, unless the applicable agreement or configuration specifies otherwise.
At the end of the applicable retention period, information is deleted or otherwise handled under approved procedures. Authorized training or testing datasets are subject to project-specific retention and deletion requirements. Backup copies may persist until the backup retention cycle expires. Client-managed infrastructure remains subject to the client’s own backup and disposal responsibilities.
10. Confidentiality and Third-Party Disclosure
We treat client technical, business, and operational information as confidential and do not sell, rent, or commercially distribute it. Information may be shared with approved personnel, authorized service providers, designated client representatives, or pursuant to a legally valid requirement. Permitted third-party access is subject to appropriate security and contractual safeguards. Where legally permitted, we notify clients of compelled disclosures in accordance with applicable agreements.
11. International Data Transfers and Residency
Data residency and permitted international transfers are established according to client requirements and contracts. Where cross-border processing is necessary, we apply relevant contractual, organizational, and technical safeguards and obtain the required authorizations, except where applicable law permits or requires otherwise.
12. Backup and Disaster Recovery
For company-managed environments, backup and recovery follow applicable operational procedures and contractual commitments. For client-managed on-premises deployments, the client may be responsible for infrastructure backup and disaster recovery. Recovery objectives and responsibilities are defined in the applicable agreements and recovery arrangements.
13. Security Incident and Data Breach Management
We maintain procedures to identify, assess, contain, investigate, and remediate information security incidents. Where a confirmed incident affects client information, we take appropriate mitigation measures, communicate with affected clients according to applicable legal and contractual notification requirements, cooperate in investigation, and implement appropriate corrective actions.
14. Individual Privacy Rights
Depending on applicable law, individuals may have rights relating to access, correction, deletion, or restriction of the processing of their personal information. Where we process information on a client’s behalf, requests relating to the client’s workforce, surveillance systems, and operational data should ordinarily be directed to that client. We provide reasonable assistance subject to law, contractual terms, and technical feasibility.
15. AI Model Development and Data Usage
Client-provided videos, images, and operational datasets are not automatically incorporated into general-purpose or externally distributed AI training datasets. Model customization, validation, testing, or development using client material requires appropriate authorization and is governed by the agreed project scope and relevant confidentiality, access, retention, and security controls.
16. Website Cookies and Similar Technologies
Our website may use necessary cookies or similar technologies to support functionality and security. Optional analytics or tracking tools, where used, are subject to applicable privacy notices and consent requirements. Visitors may manage cookies in their browser settings, which may affect certain website functions.
17. Employee and Workplace Privacy
SafetyLens is intended to support workplace safety and operational risk monitoring. Clients deploying CCTV are responsible for meeting applicable workplace privacy, employment, surveillance, notice, and authorization requirements. We process monitored information within the authorized service scope.
18. ISO/IEC 27001:2022 Certification and Governance
The Disrupt Labs is certified to ISO/IEC 27001:2022 by EBS Registrars LLC. This certification demonstrates that an information security management system has been assessed against the standard within the certification’s stated scope. It does not independently certify every individual product, infrastructure component, or client deployment.
Our ISMS addresses information security risk management and the protection of confidentiality, integrity, and availability through appropriate governance, policies, access management, supplier controls, incident response, internal review, and continual improvement.
19. Changes to This Privacy Policy
We may revise this Privacy Policy in response to changes in services, technologies, operations, or applicable requirements. Updated terms will be published on our website, and material changes affecting client processing may be communicated through applicable contractual channels.
20. Contact Information
The Disrupt Labs – SafetyLens
Privacy and Information Security Contact: info@thedisruptlabs.com
Website: https://thedisruptlabs.com
Subject: Privacy and Data Protection Inquiry
We are committed to addressing legitimate privacy and information security concerns in accordance with applicable requirements and contractual obligations.